Card Rails
A rail is the way an order intent gives a payment credential to a merchant. One order intent can have several rails, and the agent gets a new credential for each payment. The card network rails give the strongest protection, because the network enforces the limit:
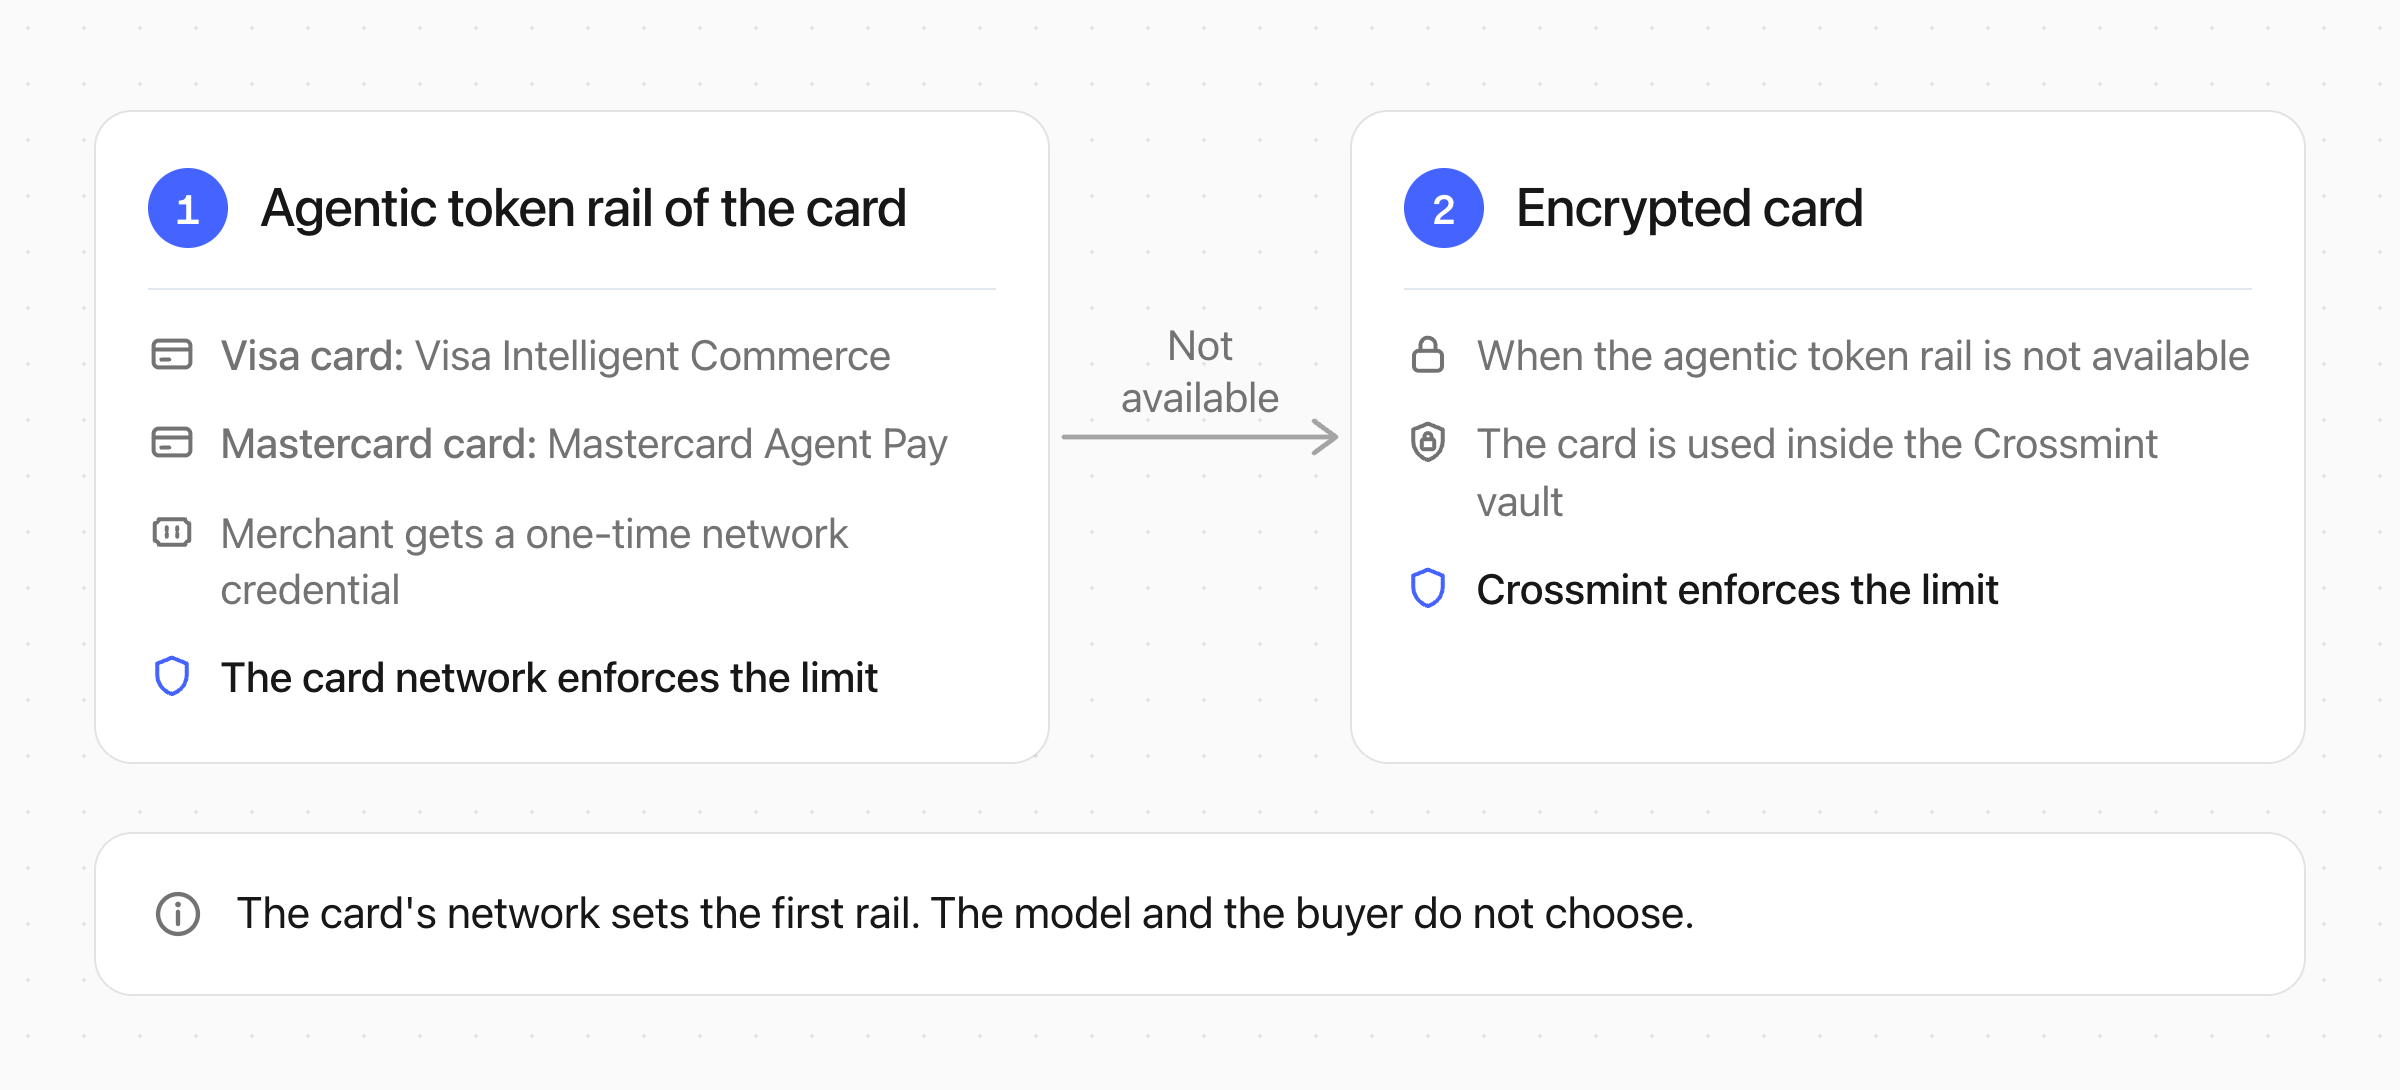
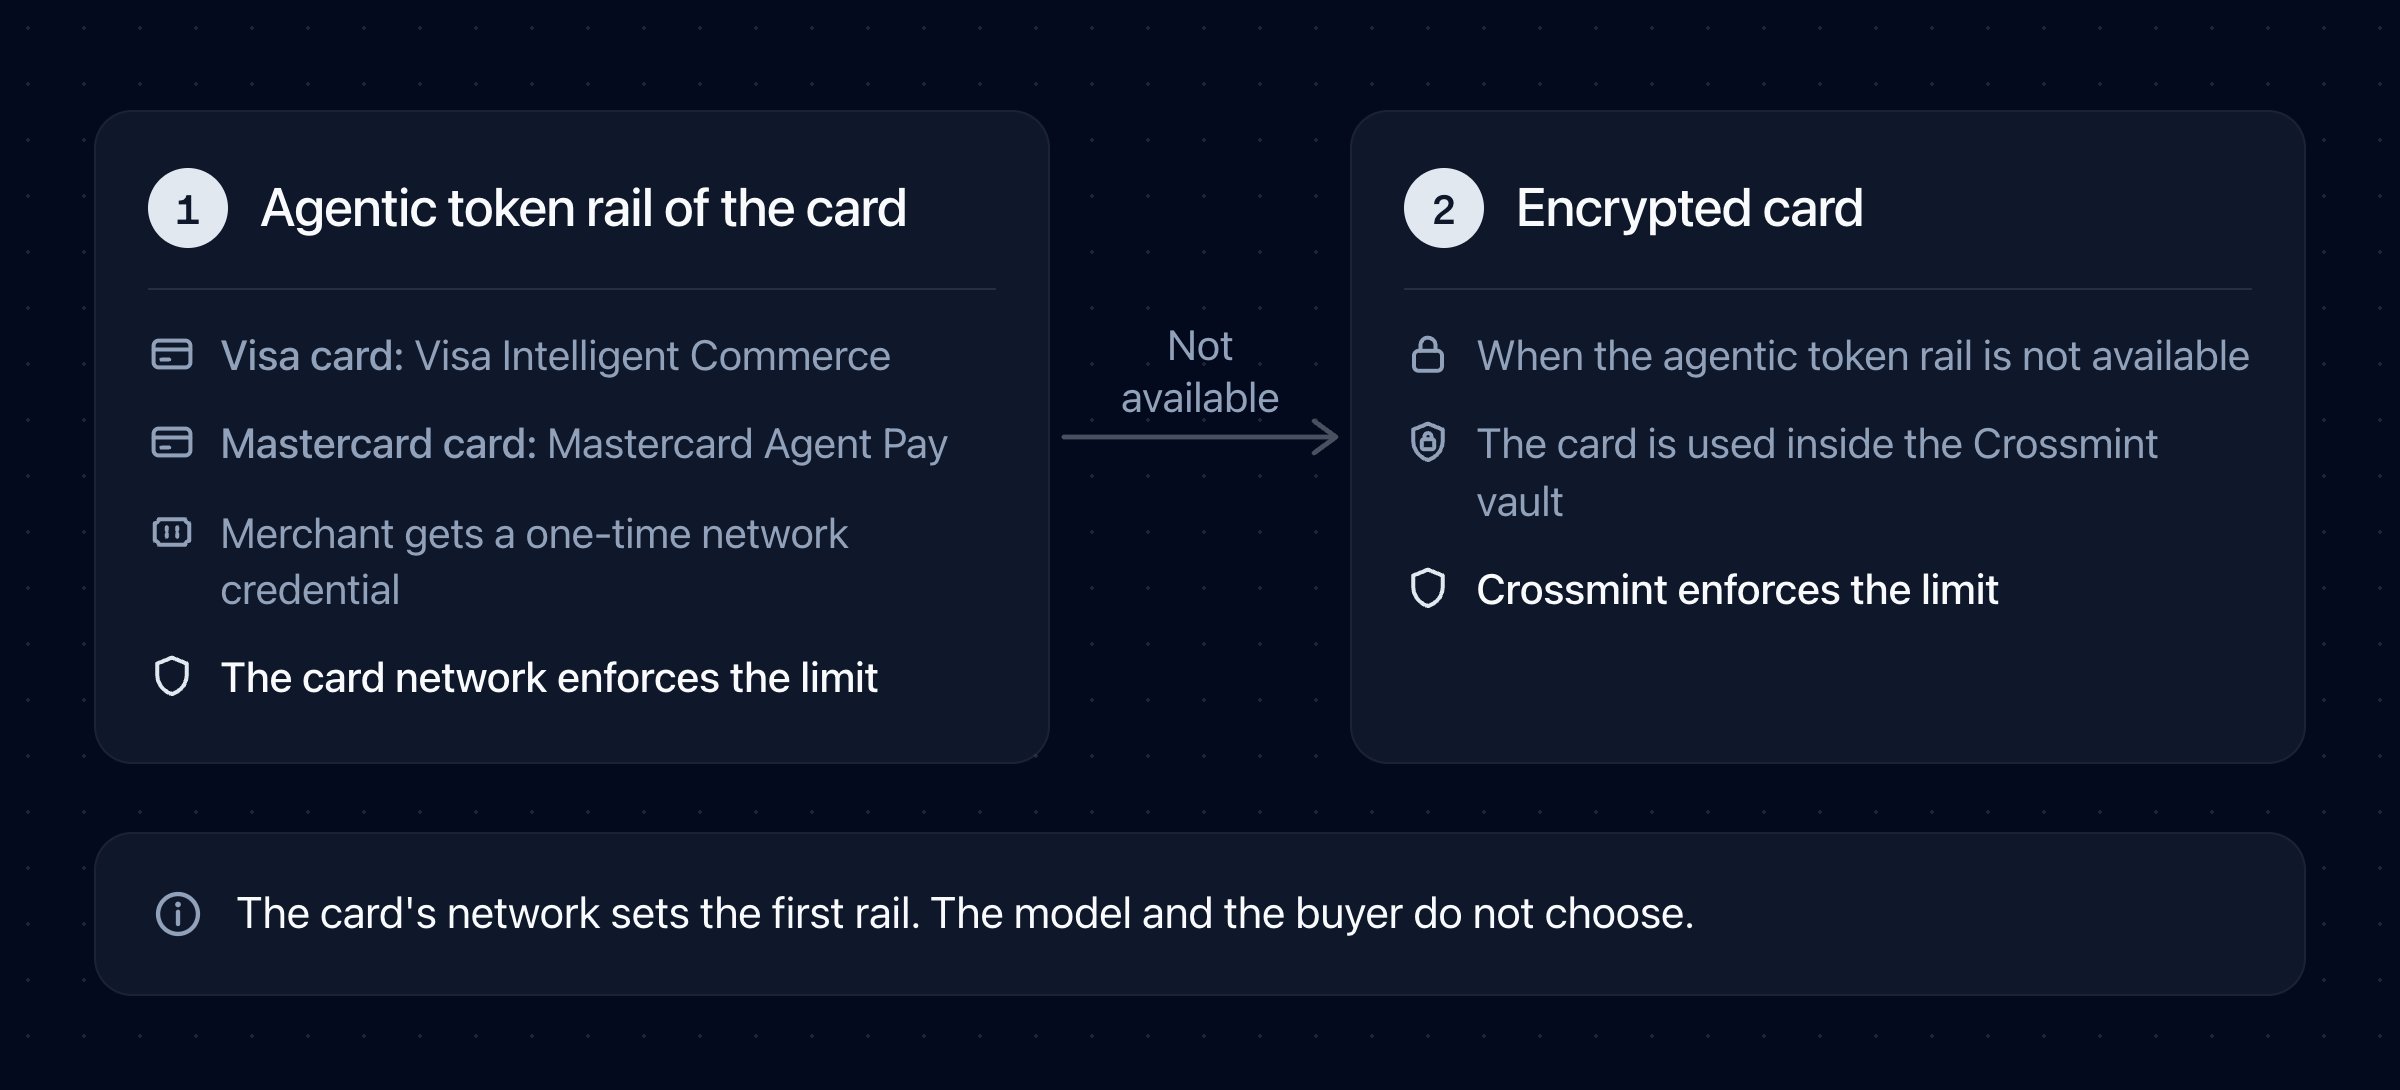
A card gets a network rail when it is enrolled in Visa Intelligent Commerce or Mastercard Agent Pay. See the eligible cards in the Agent Cards Quickstart. The Stripe shared payment token works only at sellers that accept it. The encrypted card is the fallback for every other card.
How to Stay PCI Compliant
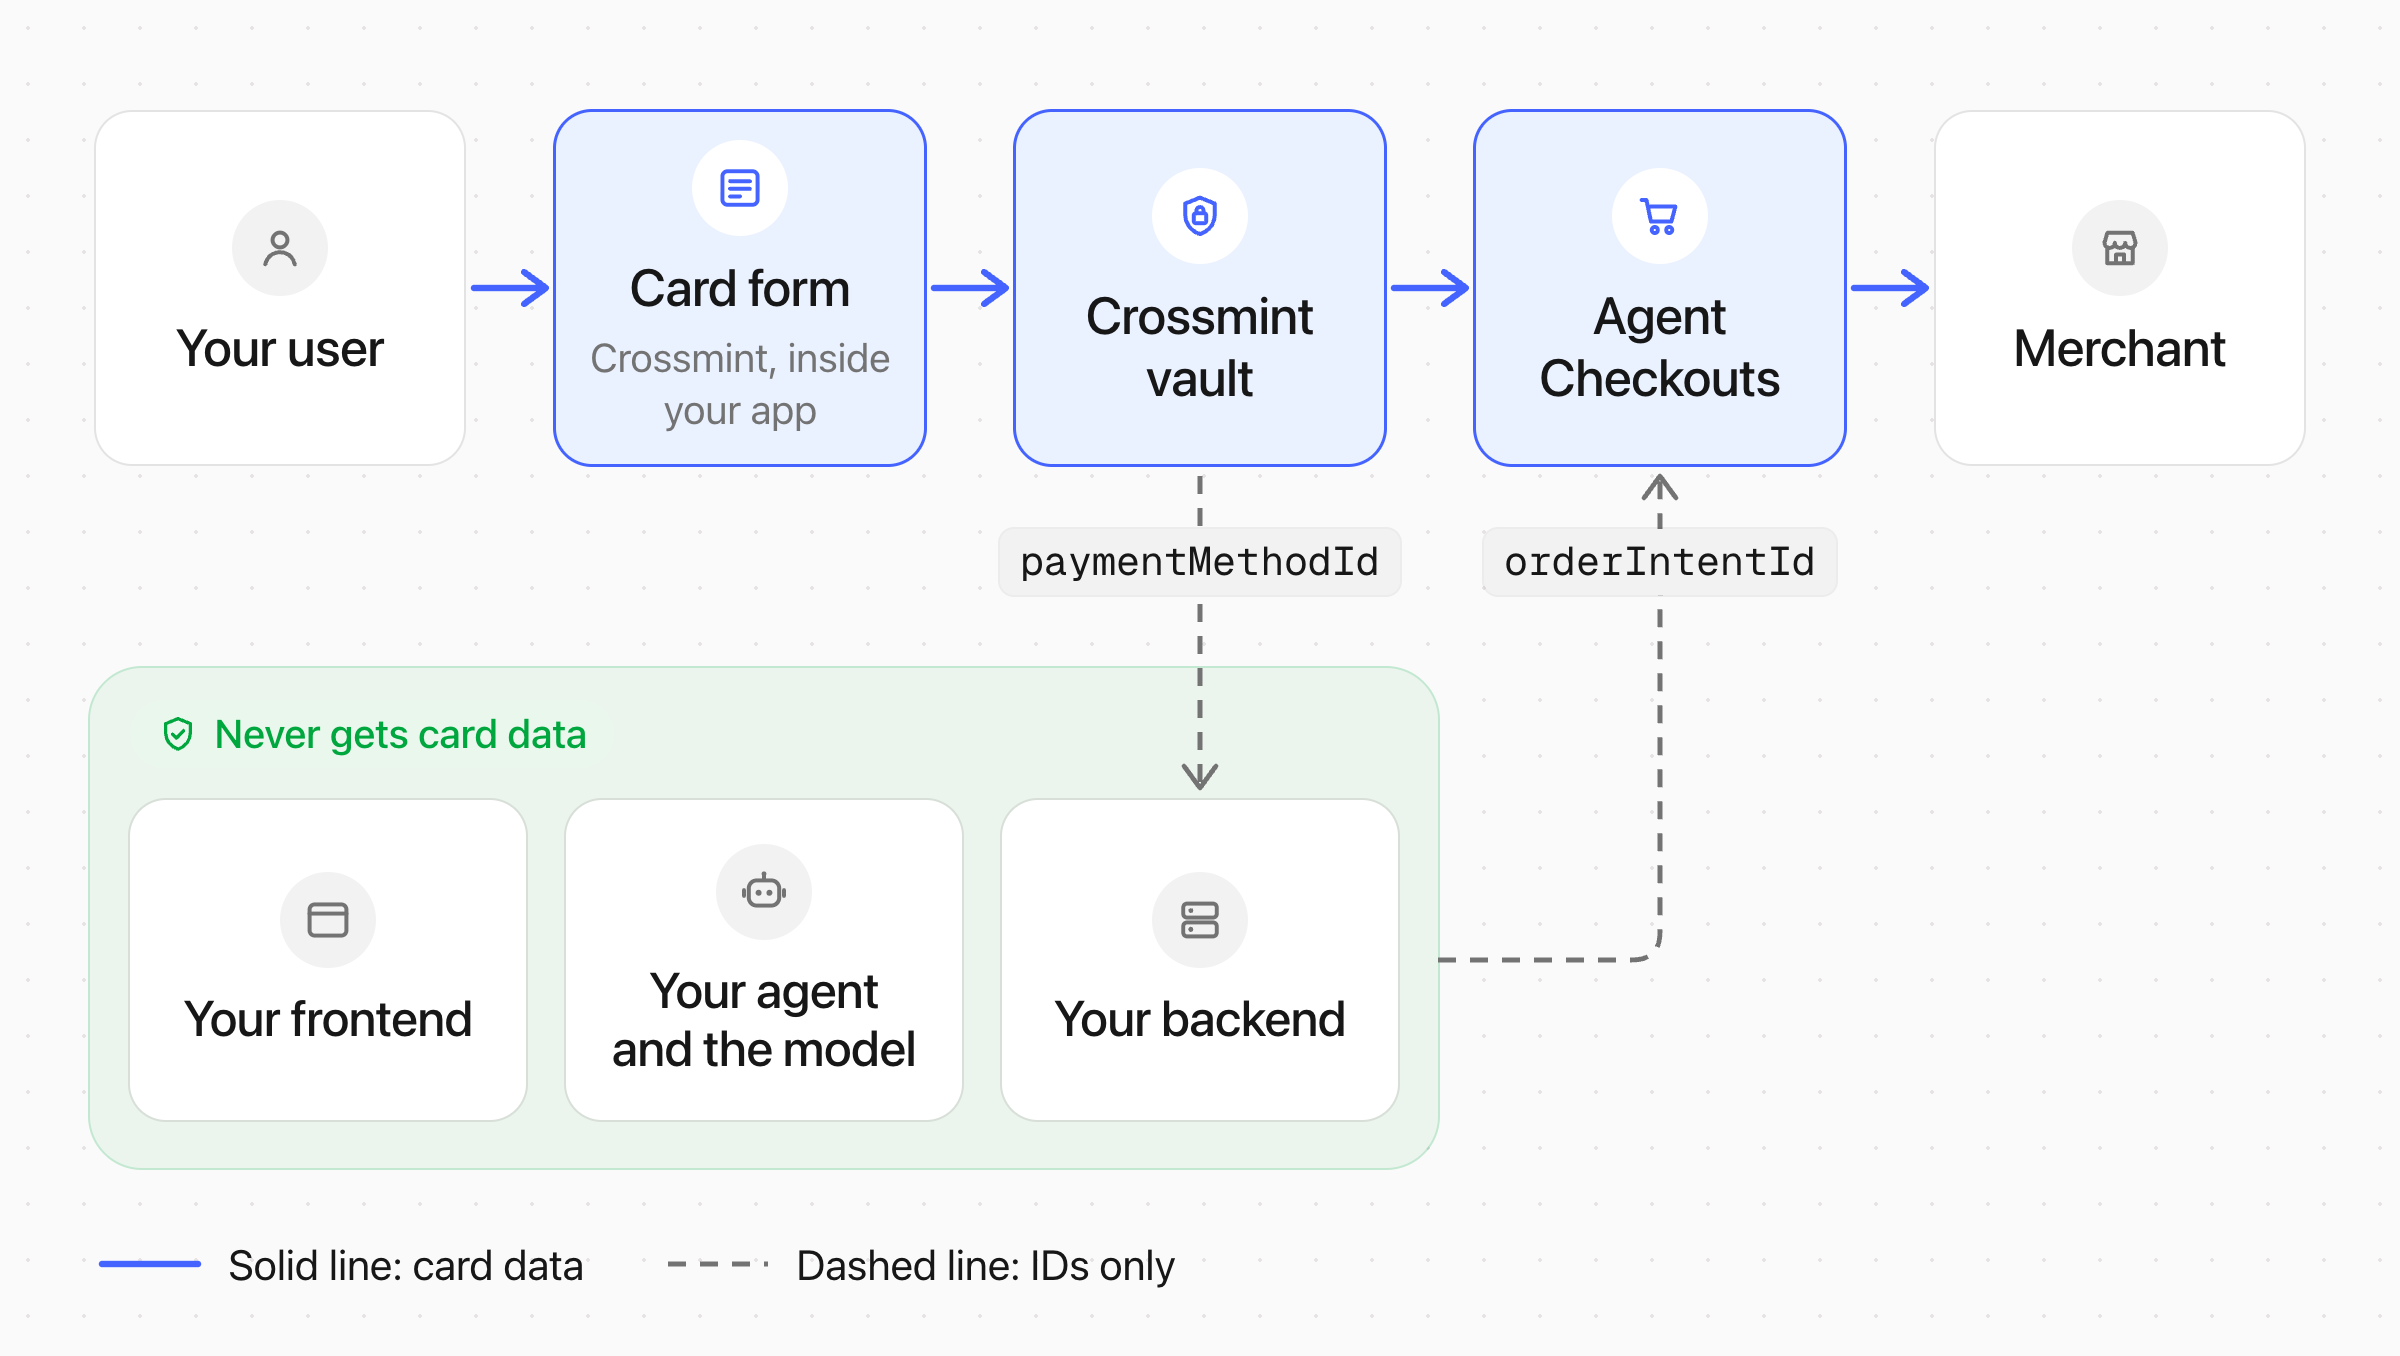
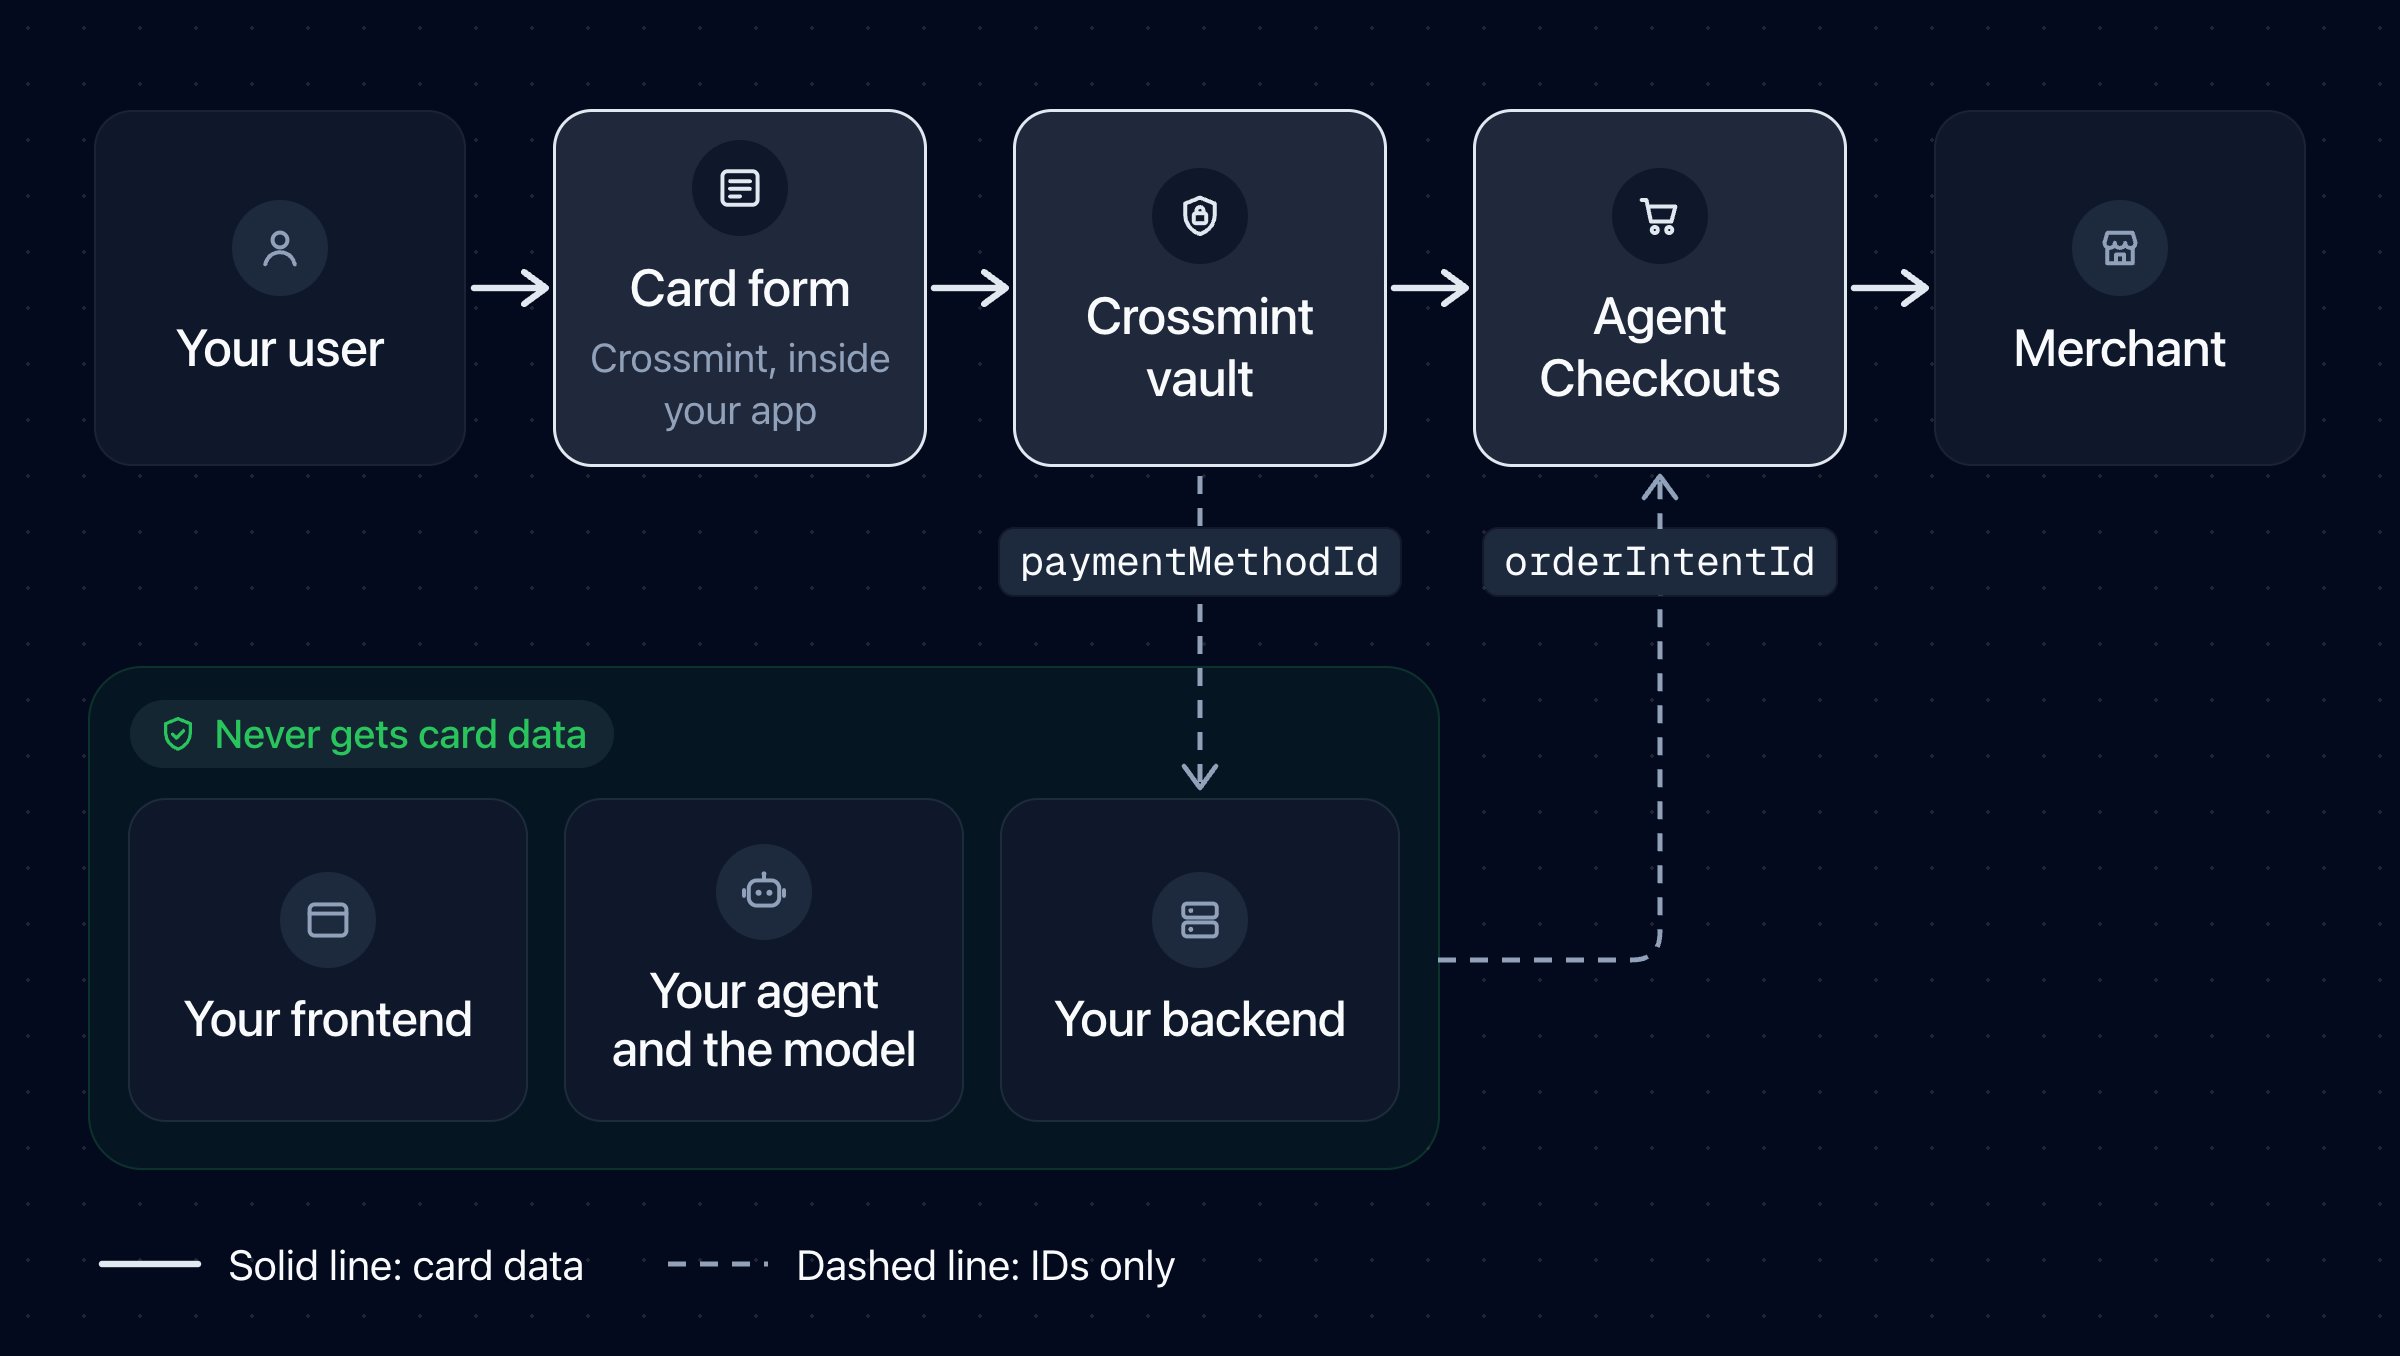
Collect cards only with the Crossmint card form. A card that a user types into your own form, or into a chat message, goes through your systems. Then pay in one of two ways.With Agent Checkouts
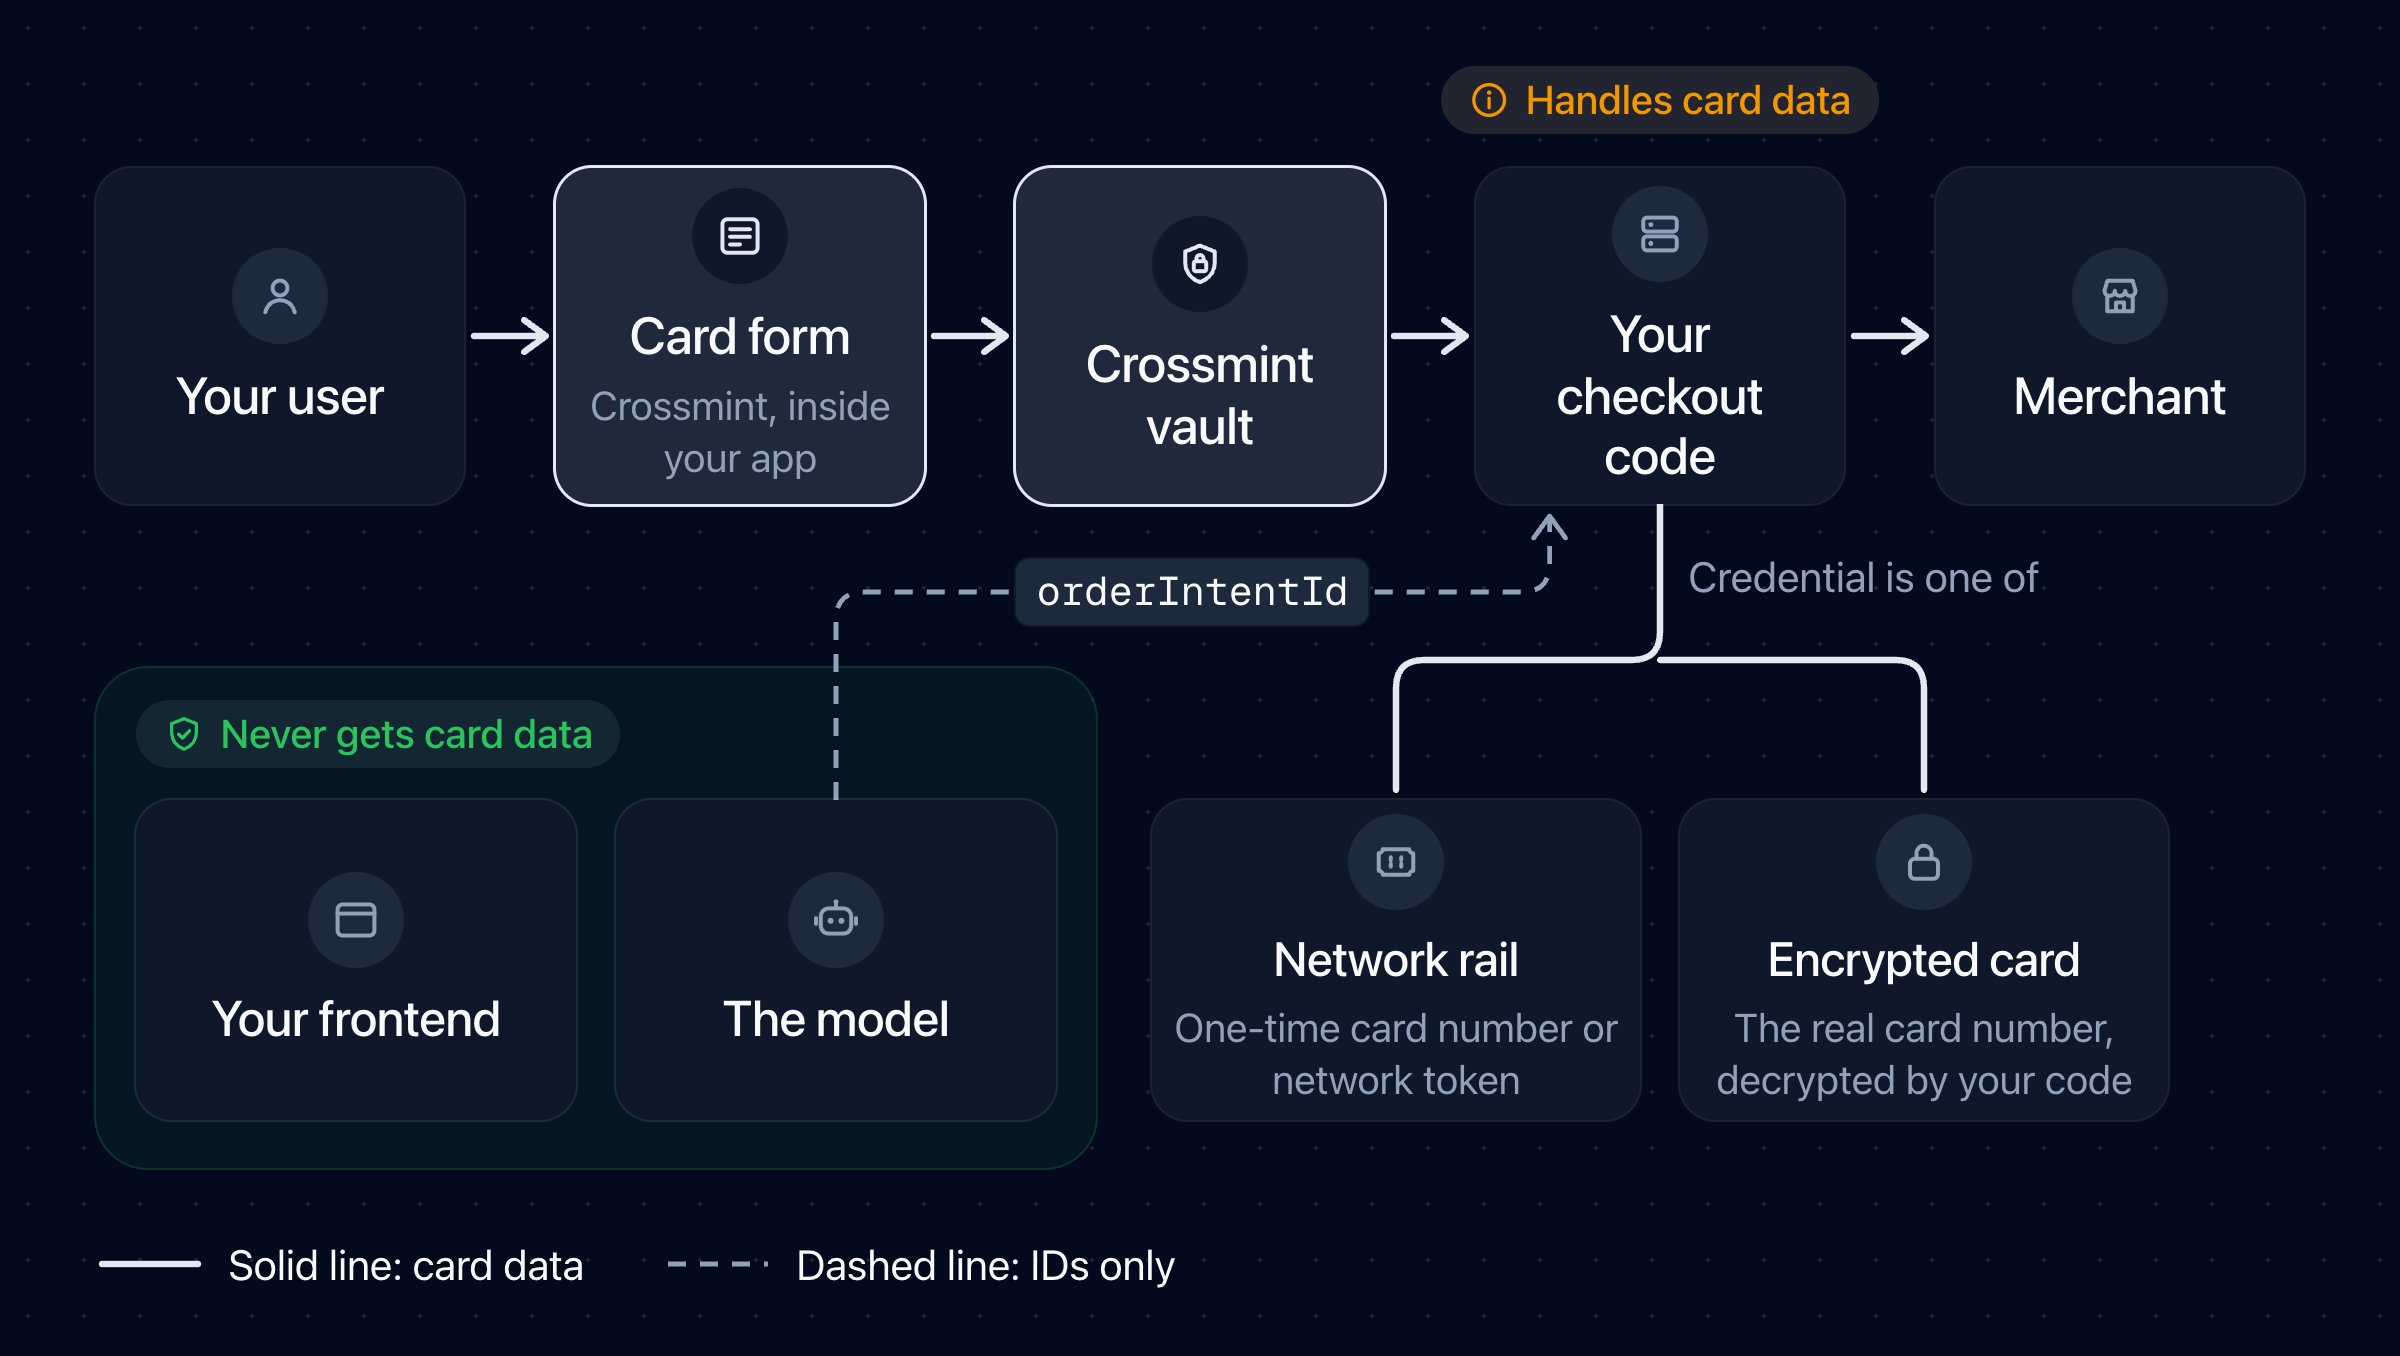
Agent Checkouts is the Crossmint API that buys on merchant websites for your user. When the checkout asks for payment, your app sends only theorderIntentId. The checkout gets the credential and enters it at the merchant inside Crossmint’s PCI-compliant systems. So the checkout can use any rail, including the encrypted card, and your app, your agent, and the model never get card data. Every saved card works, and you do not enable anything.
Agent Checkouts does not accept card details in the
task, in messages, in buyer profiles, or in form answers.
How Agent Checkouts Picks the Rail
With Your Own Checkout
With your own automation, such as your own browser agent or a merchant API, your code gets a credential from the order intent for each payment and enters it at the merchant. See Get a Card Number for the requests.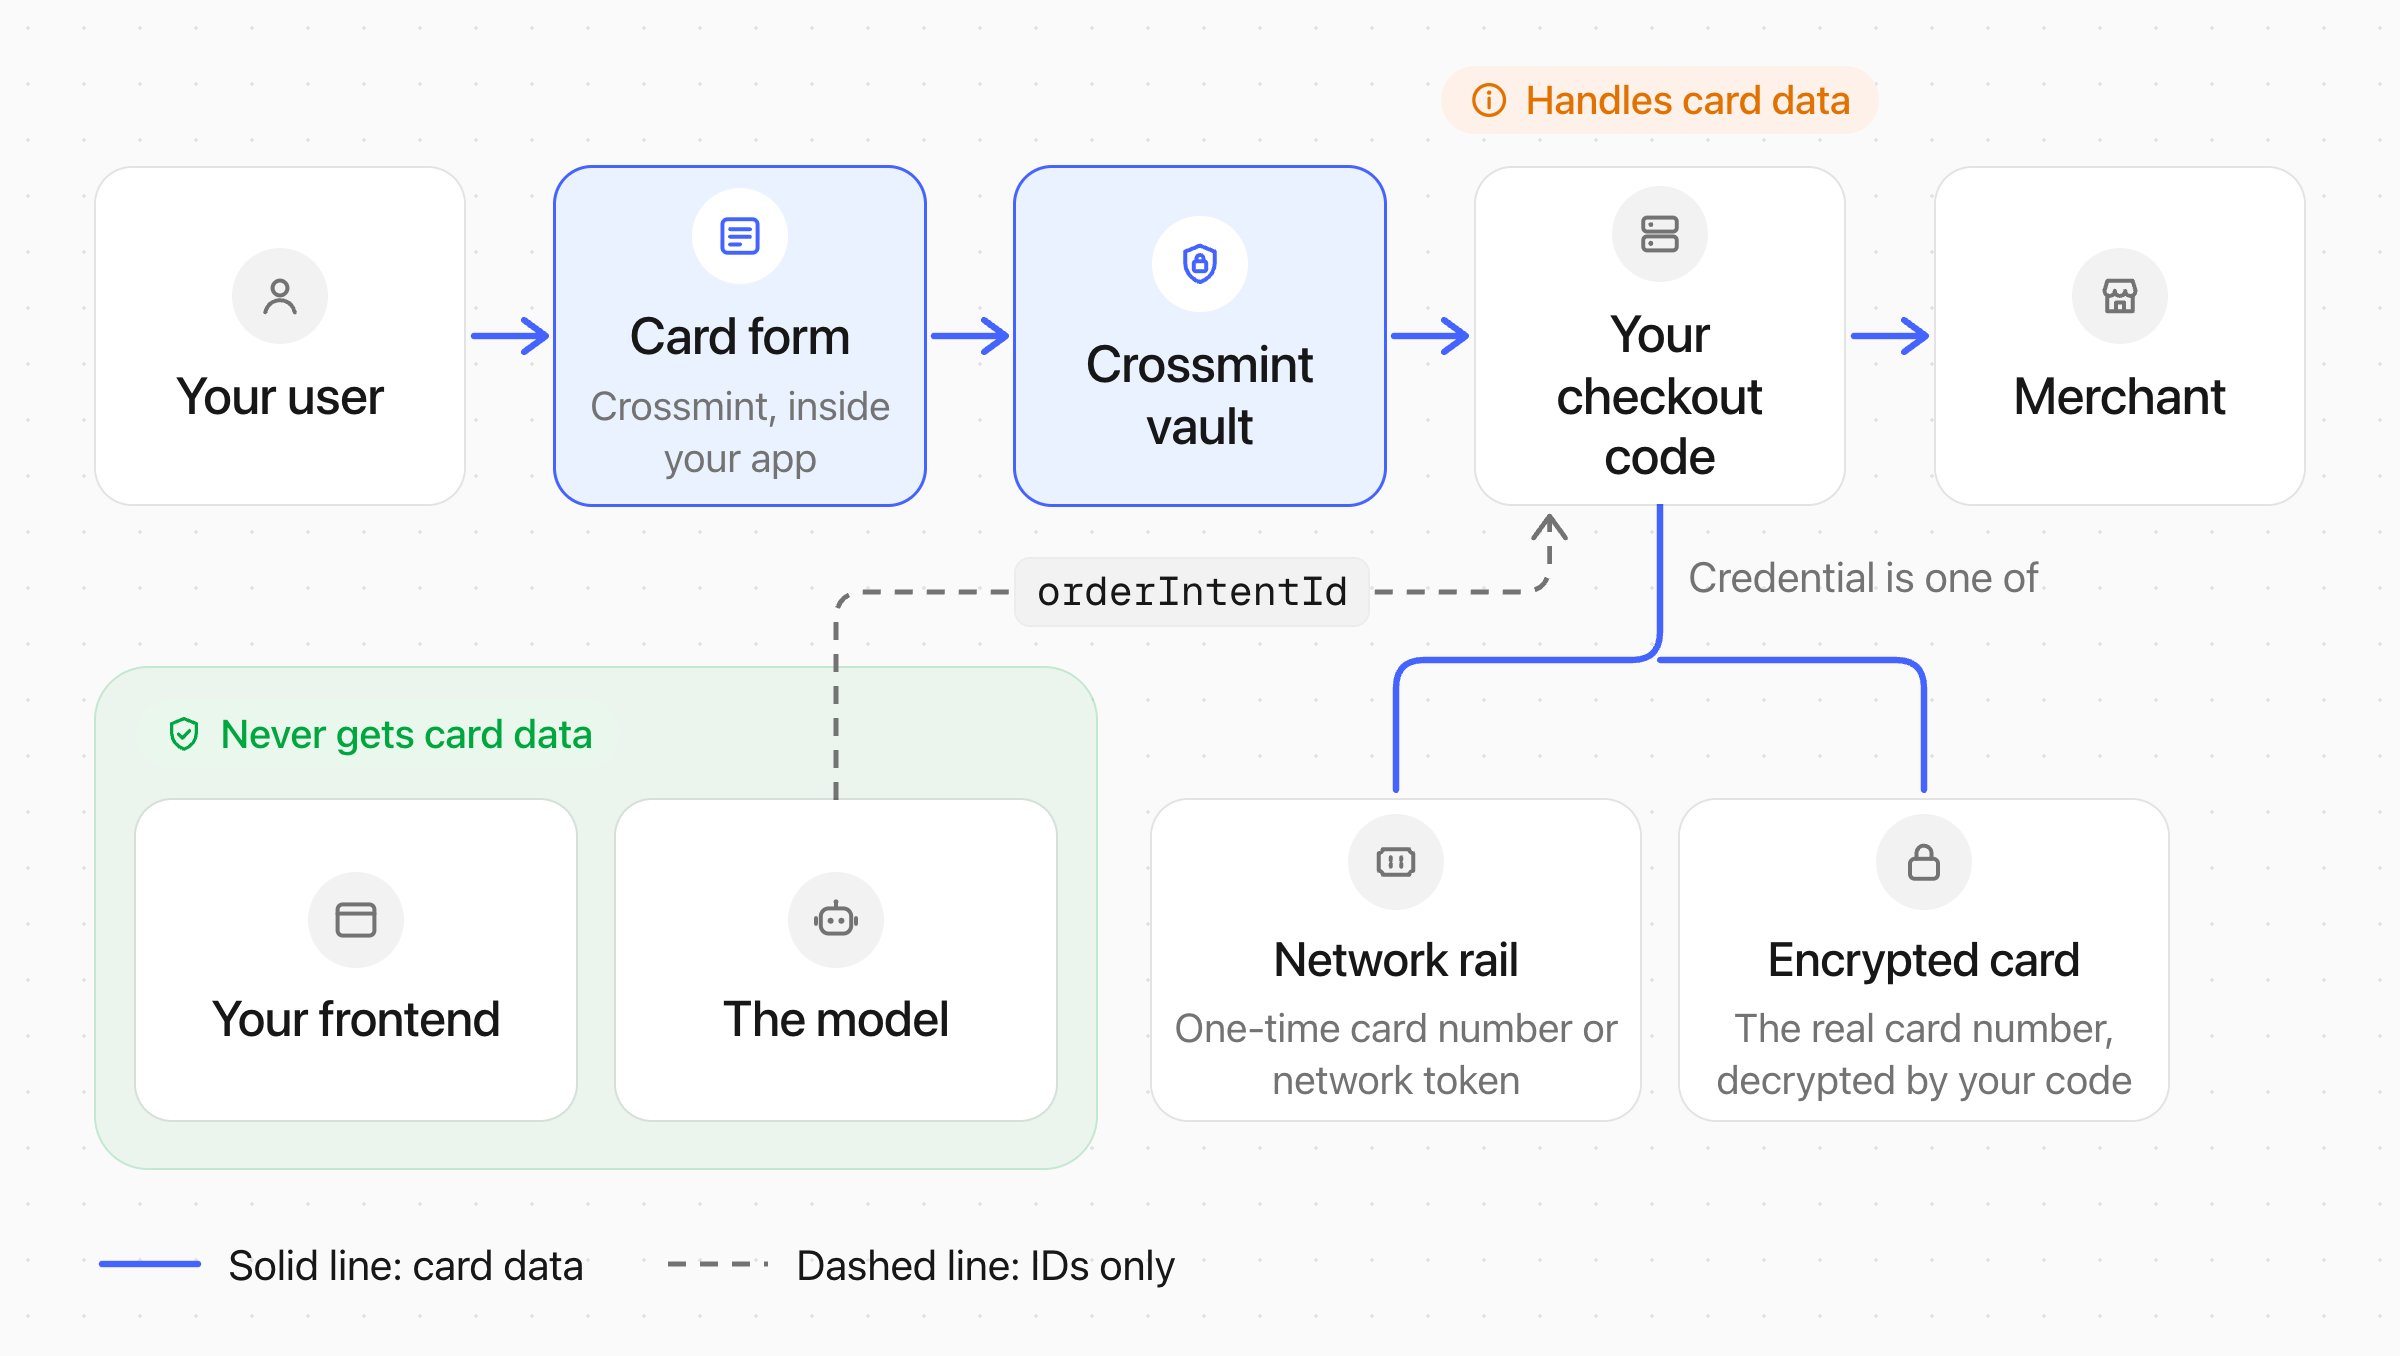
- A network rail (
rail: "agentic-token", withprovidervicoragentpay). Your code gets a one-time card number for the amount that you request, and the card network enforces the amount and the merchant. Visa considers network tokens and single-use card numbers out of PCI DSS scope. - A Stripe shared payment token (
rail: "spt"). Your code gets a token for one seller that accepts it, not card data. - The encrypted card (
rail: "encrypted-card"). Your code gets the real card number, encrypted to your RSA public key, so your setup must be PCI compliant. In production, your project also needs encrypted card access. The card network does not enforce the limit, so your code must keep each purchase within the amount that it got and the order intent’s merchant. To set up the encrypted card for your own automation, contact us.
active, and the encrypted card only when no network rail can be used. Let your code, not the model, enter the credential in the merchant’s card fields. Give the model only the orderIntentId, and do not log or store the credential. Your qualified security assessor (QSA) confirms your final PCI scope.
See Also
Approve an Order Intent
Create an order intent and verify its rail
Pay for a Checkout
Answer a payment request with an order intent
Get a Card Number
Get a credential for your own checkout